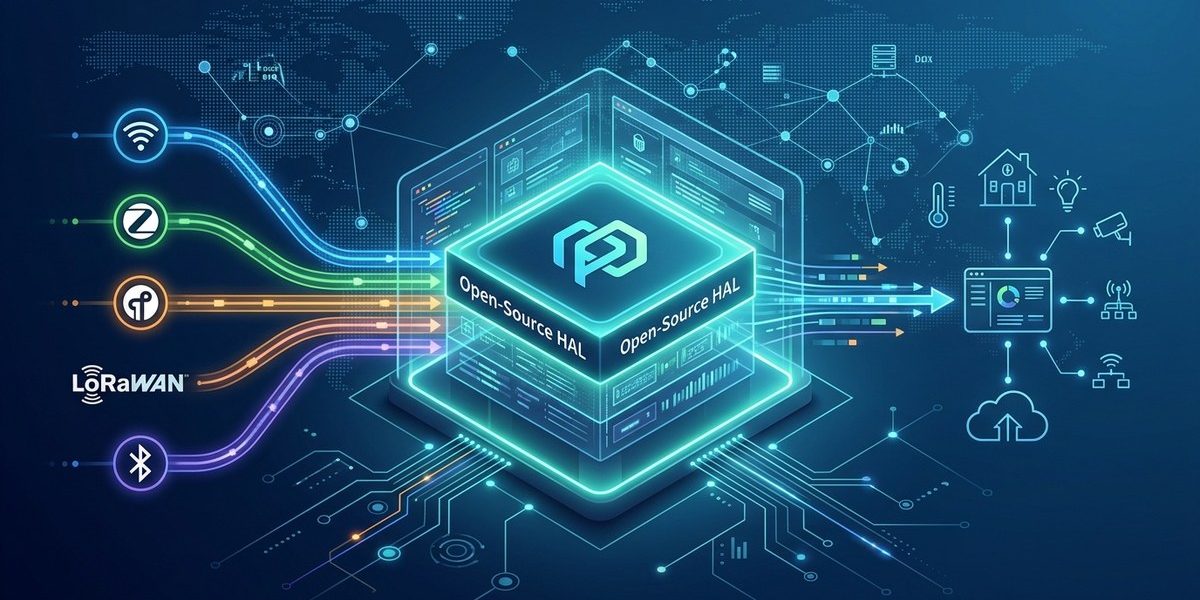
How Open-Source Hardware Abstraction Layers Simplify Multi-Protocol IoT Interoperability

The challenge is no longer about connecting a device to the internet. It is about connecting that device to every other device, on every protocol, across every vendor’s cloud, without writing a thousand lines of bespoke code. For embedded systems engineers and IoT solution architects, the pressure to support Wi-Fi, Bluetooth Low Energy, Thread, Zigbee, and Matter all at once is real. This is where the hardware abstraction layer (HAL) becomes the quiet hero. And when that HAL is open source, it changes the game for how we build, secure, and scale IoT products.
Open-source hardware abstraction layers decouple your application code from vendor-specific silicon, making multi-protocol IoT interoperability a matter of configuration rather than rewrites. By adopting a HAL, you reduce maintenance, improve security patching, and future-proof your devices for emerging standards like Matter and Thread in 2026.
Why Multi-Protocol Support Feels Like a Chore
Think about the last time you had to port an application from one microcontroller to another. The core logic was probably fine, but the peripheral drivers? Not so much. Vendor A’s GPIO API looks nothing like Vendor B’s. And do not even start on the timer modules. This is the fragmentation tax that eats engineering hours and delays product launches.
When you add wireless protocols into the mix, the pain multiplies. A single system-on-chip might support a proprietary 2.4 GHz radio, Bluetooth Low Energy, and 802.15.4. Each stack comes with its own initialization routines, callback mechanisms, and power management quirks. Without a common abstraction, your application code becomes a tangled web of #ifdef VENDOR_A preprocessor directives. It is brittle, hard to test, and a nightmare to audit for security.
Open-source HALs solve this by defining a common API for the hardware, regardless of who manufactured the chip. You write once, then compile for different targets. But how does this actually work in practice? And more importantly, how does it help you build interoperable IoT devices that talk to each other in 2026?
The Anatomy of an Open-Source HAL
A hardware abstraction layer sits between your application code and the silicon. It exposes a consistent set of functions for things like reading sensors, toggling GPIO pins, and initializing the radio. The magic is that the underlying implementation is different for each vendor, but the API signature stays the same.
Let’s look at a simple example. You need to read a temperature sensor on a custom board. With a HAL, your application calls hal_temp_read(). Under the hood, the HAL knows whether it needs to use an I2C bus, a SPI bus, or an analog pin. It handles the low-level register writes and timing diagrams. Your application does not care about the details, because it only depends on the HAL’s interface.
This is especially powerful for wireless stacks. A well-designed HAL abstracts the radio’s medium access control (MAC) layer. It provides a uniform way to send and receive packets, regardless of whether the radio is a sub-GHz transceiver or a 2.4 GHz multi-protocol chip. This is the foundation for building interoperable smart devices using open-source technologies.
The Zephyr and Mbed Approach
When we talk about open-source HALs in 2026, two names dominate the conversation: Zephyr and Mbed OS. Both are Linux Foundation projects with vibrant communities and commercial backing. They take slightly different approaches, but the goal is the same: make it easy to write portable embedded code.
Zephyr, for instance, uses a device tree to describe the hardware. The device tree tells the kernel which peripherals are present, their memory addresses, and their interrupt lines. The HAL then uses this information to configure the hardware correctly. This is a massive win for interoperability because the same application binary can run on different boards without recompilation, as long as the device tree is updated.
Mbed OS, on the other hand, uses a more object-oriented C++ API. It is incredibly approachable for developers coming from a higher-level software background. The HAL abstracts everything from digital I/O to the network socket interface. For rapid prototyping and building secure smart devices with open-source IoT frameworks, Mbed is often the first choice.
How a HAL Simplifies Multi-Protocol Support
The real value of a HAL shines when you need to support multiple protocols on a single device. Consider a smart home gateway. It needs to talk to Wi-Fi devices, Bluetooth Low Energy sensors, and Zigbee or Thread end-nodes. Without a HAL, you are juggling three different radio stacks, each with its own threading model and event loop.
A HAL unifies these. It provides a single, consistent interface for sending and receiving frames, regardless of the underlying radio. This means your application can route a message from a Thread node to a Wi-Fi client without caring about the physical layer. The HAL handles the translation.
Here is a practical process for implementing this in your next project:
- Define the abstraction boundary: List the operations your application needs from the radio. This might include
init,send,receive,set_channel, andget_rssi. Keep it minimal. Do not abstract the entire radio, just the parts your app uses. - Select a HAL with multi-protocol support: Look for a HAL that has first-class support for the wireless stacks you plan to use. Zephyr, for example, has native support for Wi-Fi, BLE, 802.15.4, and Thread.
- Implement the vendor-specific shims: For each target platform, write a small shim that maps the HAL’s API to the vendor’s SDK. This is where the vendor-specific code lives, and it is the only part you need to write and maintain.
- Test against a reference platform: Use a well-supported board as your reference. Compile your application against the HAL and run your test suite. This catches portability bugs early.
- Automate hardware-in-the-loop testing: Set up a CI pipeline that flashes your firmware onto real hardware and runs a smoke test. This verifies that your HAL abstraction holds up across different physical devices.
Interoperability Beyond the Wire
Interoperability is not just about the physical radio. It is also about the data format, the application layer, and the discovery mechanism. A HAL helps with the lower layers, but you still need a common language for the upper layers. This is where open standards like Matter and the open-source protocols that enhance security and interoperability in IoT devices come into play.
Matter, formerly known as Project Connected Home over IP (CHIP), is an open-source application layer that runs on top of Wi-Fi, Thread, and Bluetooth Low Energy. It defines a data model, a set of clusters, and a common interaction model. By building your device on top of a HAL and implementing the Matter stack, you guarantee that it will work with any other Matter-certified device, regardless of the vendor.
The combination of an open-source HAL and an open application layer is the backbone of secure, interoperable IoT. It removes the need for proprietary gateways and closed ecosystems. Your device can join any network, talk to any cloud, and integrate with any smart home platform.
Security Benefits of a Hardware Abstraction Layer
Security is often cited as the top concern for IoT deployments. A HAL can actually improve your security posture in several ways. First, it centralizes the security-critical code. Instead of scattering security checks throughout your application, you can enforce them in the HAL. For example, the HAL can validate that a received frame passes a Message Integrity Check (MIC) before handing it up to the application.
Second, a HAL makes it easier to update the radio stack. When a vulnerability is found in a wireless protocol, you only need to update the HAL’s implementation, not the entire application. This reduces the risk of introducing regressions during a security patch. This is a key reason why open-source firmware updates reduce IoT attack surfaces.
Third, open-source HALs benefit from constant review. With thousands of developers looking at the code, vulnerabilities are more likely to be spotted and fixed quickly. This is a stark contrast to closed-source binary blobs, where you are relying on the vendor’s internal security team. The transparency of open source is a powerful tool in the fight against malicious actors, especially when you consider how open source can help meet IoT security regulations in 2026.
Common Mistakes When Adopting a HAL
Adopting a HAL is not a silver bullet. It requires discipline and a clear understanding of the trade-offs. Here are some common pitfalls and how to avoid them.
| Mistake | Why It Happens | How to Avoid It |
|---|---|---|
| Over-abstraction | Trying to abstract every single feature of the hardware | Only abstract what your application uses. Keep the API surface small and focused. |
| Ignoring the device tree | Treating the device tree as an afterthought | Use the device tree as the single source of truth for hardware configuration. |
| Writing custom shims too early | Not validating the HAL API against real hardware | Prototype on a reference board first. Then write the vendor-specific shims. |
| Skipping hardware-in-the-loop testing | Relying solely on unit tests and simulation | Automate tests that run on physical devices to catch integration issues. |
| Not contributing back | Using the HAL without fixing bugs | Upstream your fixes. This reduces your maintenance burden in the long run. |
Expert Advice: “The moment you find yourself writing a vendor-specific
#ifdefin your application code, you have a design problem. Your application should not know or care which radio is on the board. If it does, your HAL is leaking abstraction. Step back and refactor the interface before you go any further.”
The Role of Open-Source Communities
One of the biggest advantages of using an open-source HAL is the community behind it. When you choose Zephyr or Mbed, you are not just getting a library. You are getting a support network, a roadmap, and a pool of talent to draw from. The community is constantly adding support for new microcontrollers, fixing bugs, and improving performance.
This is especially valuable for leveraging open-source embedded frameworks to accelerate IoT innovation. You can tap into the collective knowledge of engineers who have already solved problems you are just encountering. You can also influence the direction of the project by participating in the design discussions and contributing code.
Furthermore, open-source communities are often at the forefront of security research. They are quick to respond to new vulnerabilities and proactive in developing mitigations. For a deep dive into how this works, you can explore how open-source communities accelerate IoT innovation and the role they play in building interoperable embedded platforms for next-gen smart devices.
Future-Proofing Your Design in 2026 and Beyond
The IoT landscape is changing fast. Matter is gaining traction. Thread is becoming the mesh networking standard of choice for smart home. And new wireless technologies are emerging on the horizon. In this environment, the last thing you want is to be locked into a single vendor’s SDK.
An open-source HAL is your insurance policy. It decouples your application from the underlying hardware, allowing you to pivot to new radios or microcontrollers as the market evolves. This is why open source is the foundation for trusted IoT ecosystems. It gives you the flexibility to adapt without a complete rewrite.
When you are evaluating a HAL, look beyond the initial feature list. Consider the long-term health of the project. Is the community active? Are there regular releases? Is there a clear governance model? A vibrant ecosystem is more valuable than a feature-rich but stagnant codebase.
Putting the HAL to Work
So, how do you get started? Begin by identifying a pilot project. Choose a device that requires multi-protocol support, such as a smart plug that needs both Wi-Fi and Thread. Set up the Zephyr or Mbed development environment. Port a simple example, like the Blinky or a basic radio test. Once that is working, start building your application on top of the HAL’s API.
You will likely encounter some friction. The HAL might not expose a feature you need, or you might find a bug in the implementation. Do not be afraid to dig in and fix it. That is the beauty of open source. You have the freedom to make it work for you.
As you gain confidence, you can start contributing your fixes and improvements back to the community. This not only helps others but also ensures that your changes are maintained in future releases. It is a virtuous cycle that benefits everyone.
Measuring Success Beyond the Lab
Interoperability is not a one-time achievement. It is an ongoing commitment. You need to verify that your device remains interoperable as both your firmware and the ecosystem evolve. This means participating in interoperability events, using standard test tools, and keeping an eye on the latest protocol specifications.
In 2026, we are seeing a shift towards automated interoperability testing. Projects like the Thread Group’s test harness and the Connectivity Standards Alliance’s test suite are becoming more accessible. By integrating these into your CI pipeline, you can catch regressions before they reach the field.
Remember, the goal is not just to ship a device. It is to ship a device that enhances the interoperability of IoT systems with open-source solutions. It is to build something that works well with others, that respects user privacy, and that can be trusted with sensitive data.
A Final Word on the Journey Ahead
The path to multi-protocol interoperability is not always straightforward. It requires careful planning, a willingness to learn, and a bit of patience. But the tools have never been better. Open-source HALs have matured to the point where they are not just viable for production; they are often the preferred choice for forward-thinking teams.
By embracing the open-source embedded frameworks that fortify IoT security and the HALs that tie them together, you are setting your projects up for success. You are building devices that are more secure, more flexible, and more likely to stand the test of time.
So, take the first step. Pick a board, pick a HAL, and start experimenting. The developer’s guide to open-source embedded security for smart devices is a great place to start. And as you build, remember that you are not just writing code. You are contributing to a more open, interconnected, and secure world. The future of IoT is interoperable, and with open source, that future is in your hands.